Privacy, Data Protection & Regulatory Compliance
We help organizations determine which privacy requirements apply, build the program to meet them, and maintain the evidence that it works. Our support covers Canada, the United States and activities subject to GDPR.
Coverage: PIPEDA · Quebec Law 25 · CCPA/CPRA · HIPAA · GLBA · GDPR
Services We Provide
From a single assessment to ongoing program management, we support the full lifecycle of personal information.
Privacy Program & Governance
Establish governance, policies and controls with clear ownership and evidence that the program operates. We build data inventories, processing records, classification frameworks and retention schedules to support regulatory assessments, data minimization and stronger information governance. The work also covers privacy notices, consent and individual rights processes, internal privacy audits and role-based staff training.
Explore More
Privacy Impact Assessments, DPIAs & AI Risk
Identify privacy risk before a product, system, vendor or AI use case goes live. Each assessment delivers documented findings, risk ratings and a prioritized remediation plan, covering PIAs, GDPR DPIAs and reviews of automated decision-making.
Explore More
Third-Party, Vendor & Cloud Privacy Risk
Understand and manage the privacy risk that comes with the vendors, cloud providers and outsourced services that handle your data. We support due diligence, data processing requirements, subprocessor oversight and ongoing monitoring.
Explore More
Privacy Breach & Incident Response
Be ready before an incident occurs and supported when one does. We prepare response plans, breach assessments, notification procedures and incident registers, and support you through containment, notification and post-incident review.
Explore More
Fractional Privacy Officer & DPO Services
Add experienced privacy leadership without building a full internal function. We provide ongoing program coordination, reporting and regulatory support, delivered as a fractional Privacy Officer or DPO where role and independence requirements permit.
Explore MorePrivacy Requirements Across Three Regulatory Environments
Which requirements apply depends on where you operate, the information you handle and your role in processing it. We assess applicability before recommending controls.
Canada
- •PIPEDA
- •Quebec private-sector law / Law 25
- •Alberta PIPA
- •British Columbia PIPA
- •Ontario PHIPA and applicable health privacy laws
- •CASL and regulator guidance where relevant
United States
- •California CCPA as amended by CPRA
- •Applicable comprehensive state privacy laws
- •HIPAA / HITECH
- •GLBA Privacy & Safeguards Rules
- •FTC privacy and data-security requirements
- •State breach and specialized privacy laws where applicable
GDPR / EEA
- •Scope, roles and lawful bases
- •Transparency and individual rights
- •RoPA, DPIA and DPO support
- •Privacy by design / default
- •Processor and sub-processor governance
- •International transfers and SCCs
Privacy Expertise Across Data-Intensive Sectors
How personal information is handled differs by sector. Our approach adapts to how your organization collects and uses data.
Banking, Financial Services & FinTech
Insurance
Healthcare, Life Sciences & Clinical Research
Technology, SaaS & AI
Retail, E-commerce & Hospitality
Real Estate
Mortgage & Professional Services
Employers & Growing Businesses
One Privacy Partner.
Controls That Work in Practice.
Policy, assessment, vendor oversight, training and incident readiness are strongest when managed together. We bring them under one relationship, so your program stays consistent across Canadian, U.S. and GDPR requirements and your evidence stays current.
Coordinated
Policy, assessments, vendor oversight, training and incident response managed through one relationship.
Evidence Based
Findings and recommendations grounded in testing, documentation and applicable legislation.
Operational
Support built around how personal information actually moves through your organization.
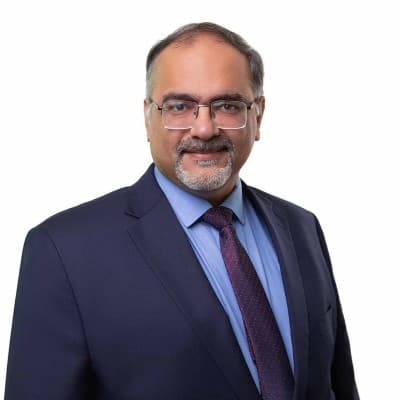
Our compliance practice is led by Manoj Ahuja, Co-Founder & Director, Compliance and Risk, who brings more than 25 years of experience across compliance, financial crime, risk, privacy, audit and finance, with senior responsibilities at ivari, Scotiabank, HSBC and MCB Bank.
Read Manoj's biography
Support Matched to the Work Required
Not every organization needs a full program build. Engagements are scoped around what you need.
- 01
Privacy Diagnostic
A focused review of applicable obligations and gaps, with prioritized recommendations.
- 02
PIA / DPIA Project
A defined assessment of a product, system, vendor, AI use case or material change.
- 03
Program Build or Remediation
Design or refresh of governance, policies, controls and procedures, with implementation support.
- 04
Managed Privacy Office
Ongoing privacy leadership, assessments, reporting and regulatory support.
- 05
Independent Review & Testing
Risk-based control testing and program effectiveness reviews, scoped to preserve independence.
- 06
Incident Support
Breach assessment, documentation, notification coordination and post-incident improvement.
Documented findings and decisions, practical templates and workflows, and a prioritized implementation or remediation plan.
A Structured Path From Requirements to Evidence
- STEP 01
Understand
We review your business, jurisdictions, personal information, systems and third parties.
- STEP 02
Map
We identify applicable obligations, data flows, risks, existing controls and the evidence required.
- STEP 03
Implement
We build or improve policies, assessments, workflows, training and reporting.
- STEP 04
Validate
We test design and operation, track corrective actions and support the program as requirements change.
Make Privacy Easier to Operate and Demonstrate
Tell us what you are building, changing or preparing for. We will confirm the relevant requirements and propose a practical scope.
Frequently Asked Questions
Supportix Global provides privacy, compliance, risk and implementation consulting. Where a formal legal opinion or jurisdiction-specific legal interpretation is required, the engagement should involve qualified legal counsel.
Yes. We assess applicability based on where you operate, your industry, the personal information you handle and your role in processing it. Legal counsel may be involved where a formal determination is required.
Yes. We build a common governance framework and map Canadian and U.S. obligations to it, while recognizing the differences between the laws.
Yes. We assess whether GDPR applies to your activities and support the controls that follow, including individual rights, processing assessments and international transfers.
Yes. Assessments can be scoped as defined projects, separate from ongoing support.
Yes. We support assessment, documentation, notification coordination and remediation. Legal counsel and forensic specialists are involved where the circumstances require them.
Where appropriate, yes. Engagements involving statutory DPO responsibilities must account for independence, reporting-line and conflict-of-interest requirements.
Not through the same team. Independence requirements apply, and a separate qualified reviewer is arranged where needed.